Lockbit Leaked Data Exclusive Content By Artists #849
Dive Right In lockbit leaked data first-class streaming. On the house on our media destination. Get lost in in a universe of content of expertly chosen media offered in HD quality, a dream come true for elite watching fanatics. With fresh content, you’ll always keep current. stumble upon lockbit leaked data curated streaming in sharp visuals for a truly engrossing experience. Hop on board our entertainment hub today to browse one-of-a-kind elite content with no payment needed, no recurring fees. Appreciate periodic new media and investigate a universe of unique creator content created for select media junkies. Don’t miss out on rare footage—get it in seconds! Treat yourself to the best of lockbit leaked data visionary original content with rich colors and hand-picked favorites.
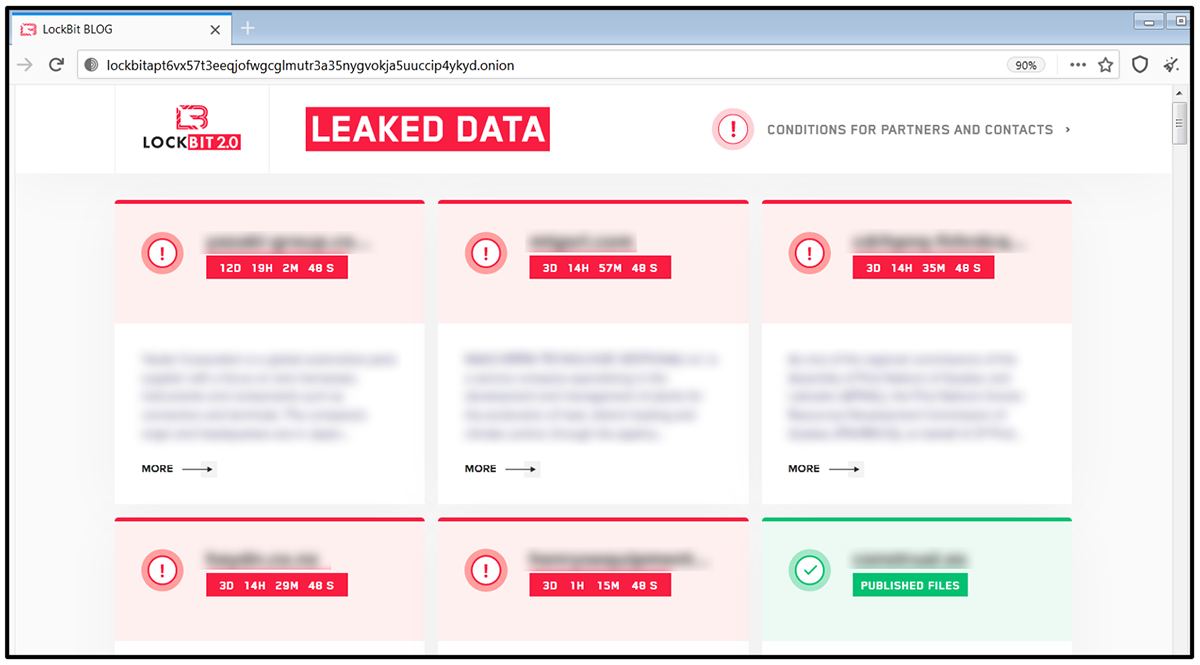
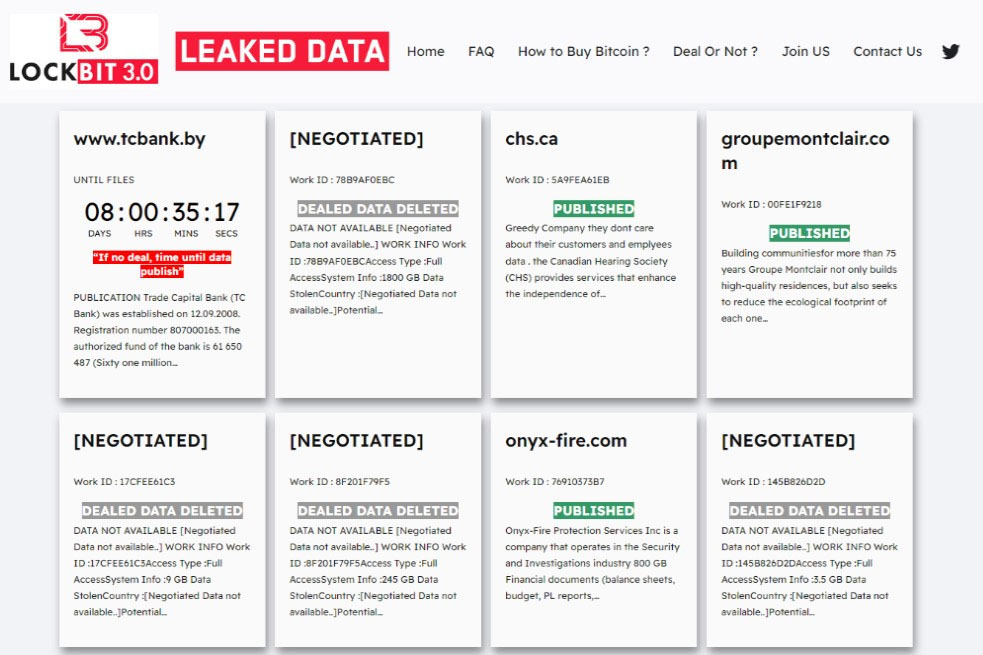
Lockbit is a cybercriminal group proposing ransomware as a service (raas). Lockbit 3.0 has been in use since at least june 2022 and features enhanced defense evasion and exfiltration tactics, robust encryption methods for windows and vmware esxi systems, and a more refined raas structure over its predecessors such as lockbit 2.0. Since january 2020, affiliates using lockbit have attacked organizations of varying sizes across an array of critical infrastructure sectors, including financial services, food and agriculture, education, energy, government and emergency services, healthcare, manufacturing, and transportation.
Meet LockBit: The Most Prevalent Ransomware in 2022 | FortiGuard Labs
According to reliaquest, the newly returned lockbit has formed a coalition with prominent raas groups dragonforce and qilin, a partnership poised to drive more frequent and effective ransomware attacks. Lockbit will automatically vet for valuable targets, spread the infection, and encrypt all accessible computer systems on a network. Law enforcement officials say they’ve identified, sanctioned, and indicted the person behind lockbitsupp, the administrator at the heart of lockbit’s $500 million hacking rampage.
No system is safe anymore
The newest variant of lockbit ransomware targets windows, linux, and vmware esxi systems simultaneously. Trend micro has sounded the alarm over the new lockbit 5.0 ransomware strain, which it warns is significantly more dangerous than past versions due to its newfound ability to simultaneously target windows, linux, and vmware esxi environments. Lockbit have created a new leak site on which they have inflated apparent activity by publishing victims targeted prior to the nca taking control of its services in february, as well as taking. Lockbit ransomware is malicious software designed to block user access to computer systems in exchange for a ransom payment